ثبت نام / ورود
0
ثبت نام / ورود
0
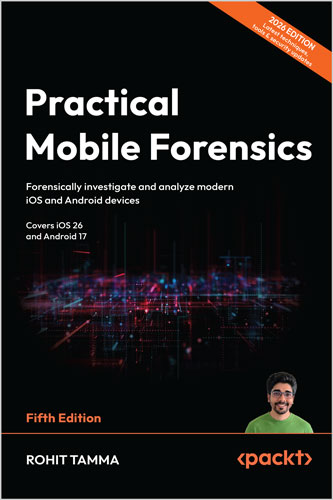
Forensically investigate and analyze modern iOS and Android devices
Rohit Tamma
#Mobile
#Forensics
#iOS
#Android
📱 تسلط عملی بر جرمیابی موبایل در iOS و Android
🔍 کتاب Practical Mobile Forensics, Fifth Edition روشهای عملی بررسی دستگاههای iOS و Android را از Data Acquisition تا Artifact Analysis و بازیابی اطلاعات پوشش میده. این ویرایش با تمرکز بر تحقیقات واقعی، کمک میکنه دادههای موبایل و اکوسیستمهای متصل به آن را با روشهایی قابلاعتماد و قابلدفاع استخراج و تحلیل کنی.
✨ ویژگیهای کلیدی
📲 نحوه استخراج و تحلیل Artifactها از دستگاههای موبایل، Cloud Ecosystemها و Backupها را آموزش میده.
♻️ تکنیکهای پیشرفته Mobile Forensics را برای بازیابی دادههای حذفشده از دستگاههای موبایل بررسی میکنه.
🔐 محدودیتهای جرمیابی در سیستمعاملهای مدرن، Encryption Modelها و روشهای عملی عبور از این محدودیتها را توضیح میده.
📘 توضیح کتاب
🧠 Mobile Forensics با گسترش Secure Hardware، اکوسیستمهای رمزگذاریشده و معماریهای Cloud-first تغییرات زیادی کرده است. کتاب Practical Mobile Forensics, Fifth Edition علم استخراج و تحلیل دادههای موبایل را بهشکلی بررسی میکنه که صحت و اعتبار Forensic آنها حفظ بشه.
📱 این ویرایش بر تکنیکهای عملی و واقعی برای بررسی دستگاههای موبایل در پلتفرمهای امروزی تمرکز داره و جدیدترین نسخههای iOS و Android را پوشش میده. مطالب کمک میکنن ساختار، Security و File System این سیستمعاملها را بهتر بشناسی.
🛠️ کتاب ابزارهای Open Source و Commercial جرمیابی را بررسی میکنه و Workflowهای ساختاریافتهای برای Acquisition، Analysis و Reporting ارائه میده. این رویکرد باعث میشه مراحل Investigation بهصورت منظم، تکرارپذیر و قابلدفاع پیش برن.
🔐 با محدودترشدن اکوسیستمهای موبایل، دسترسی به دادهها هم دشوارتر شده است. کتاب Platform-level Limitationها، Encryption Modelها و راهکارهای عملی مواجهه با این محدودیتها را تحلیل میکنه.
🧩 بخشهای پیشرفتهتر به Application Analysis، مفاهیم Reverse Engineering و روشهای شناسایی رفتارهای مخرب یا مشکوک در محیطهای Mobile اختصاص دارن. همچنین کار با System Databaseها و فرمتهای دادهای Applicationها بررسی میشه.
🎯 بعد از مطالعه کتاب، درک عملی محکمی از Mobile Forensics مدرن به دست میاری و میتونی دادههای دستگاههای موبایل و اکوسیستمهای مرتبط را با روشهایی مطمئن و قابلدفاع استخراج، تحلیل و تفسیر کنی.
🎯 چیزهایی که یاد میگیری
🔐 با معماریهای Mobile Security، شامل Encryption، Sandboxing و سازوکارهای Data Protection آشنا میشی.
📲 یاد میگیری Data Acquisition و Extraction پیشرفته را روی دستگاههای جدید iOS و Android انجام بدی.
💬 میتونی Artifactهای مهم Forensic مثل Messageها، Call Logها، App Data و System Databaseها را شناسایی و تفسیر کنی.
🗃️ یاد میگیری با SQLite Databaseها، WAL Fileها و فرمتهای رمزگذاریشده یا Encoded دادههای Application کار کنی.
🛠️ میتونی ابزارهای Open Source و Commercial جرمیابی را در Workflowهای واقعی Investigation به کار بگیری.
⚠️ محدودیتهای Mobile Forensics مدرن را درک میکنی و با راهکارهای عملی برای عبور از آنها آشنا میشی.
👤 این کتاب برای چه کسانیه؟
🔍 این کتاب برای متخصصان Digital Forensics و Investigatorهایی طراحی شده که میخوان مهارتهای بنیادی جرمیابی موبایل را در پلتفرمهای مدرن iOS و Android به دست بیارن.
🛡️ Security Professionalها، Incident Responderها و Researcherهایی که به شناخت اجزای داخلی دستگاههای موبایل، دادههای Application و تحلیل Forensic Artifactها علاقه دارن هم میتونن از مطالب کتاب استفاده کنن.
📌 آشنایی بنیادی با Digital Forensics و شناخت مقدماتی Operating Systemها کمک میکنه بیشترین استفاده را از کتاب ببری؛ بااینحال، داشتن تجربه قبلی در Forensics الزامی نیست.
📖 فهرست مطالب
فصل ۱. مقدمهای بر Mobile Forensics
فصل ۲. مروری بر معماری، Security و File System در iOS
فصل ۳. Data Acquisition از دستگاههای iOS
فصل ۴. Data Acquisition از Backupهای iOS
فصل ۵. تحلیل و بازیابی دادهها در iOS
فصل ۶. ابزارهای iOS Forensics و Automation
فصل ۷. شناخت معماری Android
فصل ۸. آمادهسازی Android Forensics و تکنیکهای پیش از استخراج داده
👤 درباره نویسنده
🔐 روهیت تاما از متخصصان Cybersecurity است و تمرکز عمیقی بر هدایت تیمهایی داره که از سازمانها در برابر حملههای سایبری محافظت میکنن.
🛡️ او بیش از ۱۷ سال سابقه فعالیت در این صنعت داره و از تجربه گسترده Technical Leadership در زمینههایی مثل Security Operations، Penetration Testing، Cloud Security و Mobile Forensics برخورداره.
🏢 روهیت تاما در حال حاضر بهعنوان Security Engineering Manager در Google فعالیت میکنه.
Master modern mobile forensics with practical techniques for iOS and Android, covering data acquisition, artifact analysis, and data recovery in real-world investigations.
Mobile forensics has evolved significantly with the rise of secure hardware, encrypted ecosystems, and cloud-first architectures. Practical Mobile Forensics, Fifth Edition explores the science of acquiring and analyzing data from mobile devices in a forensically sound manner, while addressing the challenges posed by modern operating systems and security controls.
This edition focuses on practical, real-world techniques for investigating mobile devices across contemporary platforms, including the latest versions of iOS and Android. The book covers both open-source and commercial forensic tools, guiding you through structured workflows for acquisition, analysis, and reporting. As mobile ecosystems become more restrictive, the book also examines platform-level limitations, encryption models, and practical approaches to navigate these constraints. Advanced sections introduce application analysis, reverse engineering concepts, and techniques for identifying malicious or suspicious behavior within mobile environments.
By the end of this book, you will have a strong, hands-on understanding of modern mobile forensics—enabling you to extract, analyze, and interpret data from mobile devices and associated ecosystems using reliable and defensible methods.
This book is designed for digital forensic practitioners and investigators looking to build foundational skills in mobile forensics across modern iOS and Android platforms. It is also valuable for security professionals, incident responders, and researchers interested in understanding mobile device internals, application data, and forensic artifact analysis. A foundational understanding of digital forensics and basic familiarity with operating systems will help readers get the most from this book, though prior forensic experience is not mandatory.
Rohit Tamma is a cybersecurity expert with a deep focus on leading teams that secure enterprises from cybersecurity attacks. With over 17 years in the industry, he has extensive technical leadership experience in areas like security operations, penetration testing, cloud security and mobile forensics. He currently works at Google as a Security Engineering Manager.